
Nextcloud Admins: Update or Remove the Collabora Built-in CODE App (CVE-2026-110447)
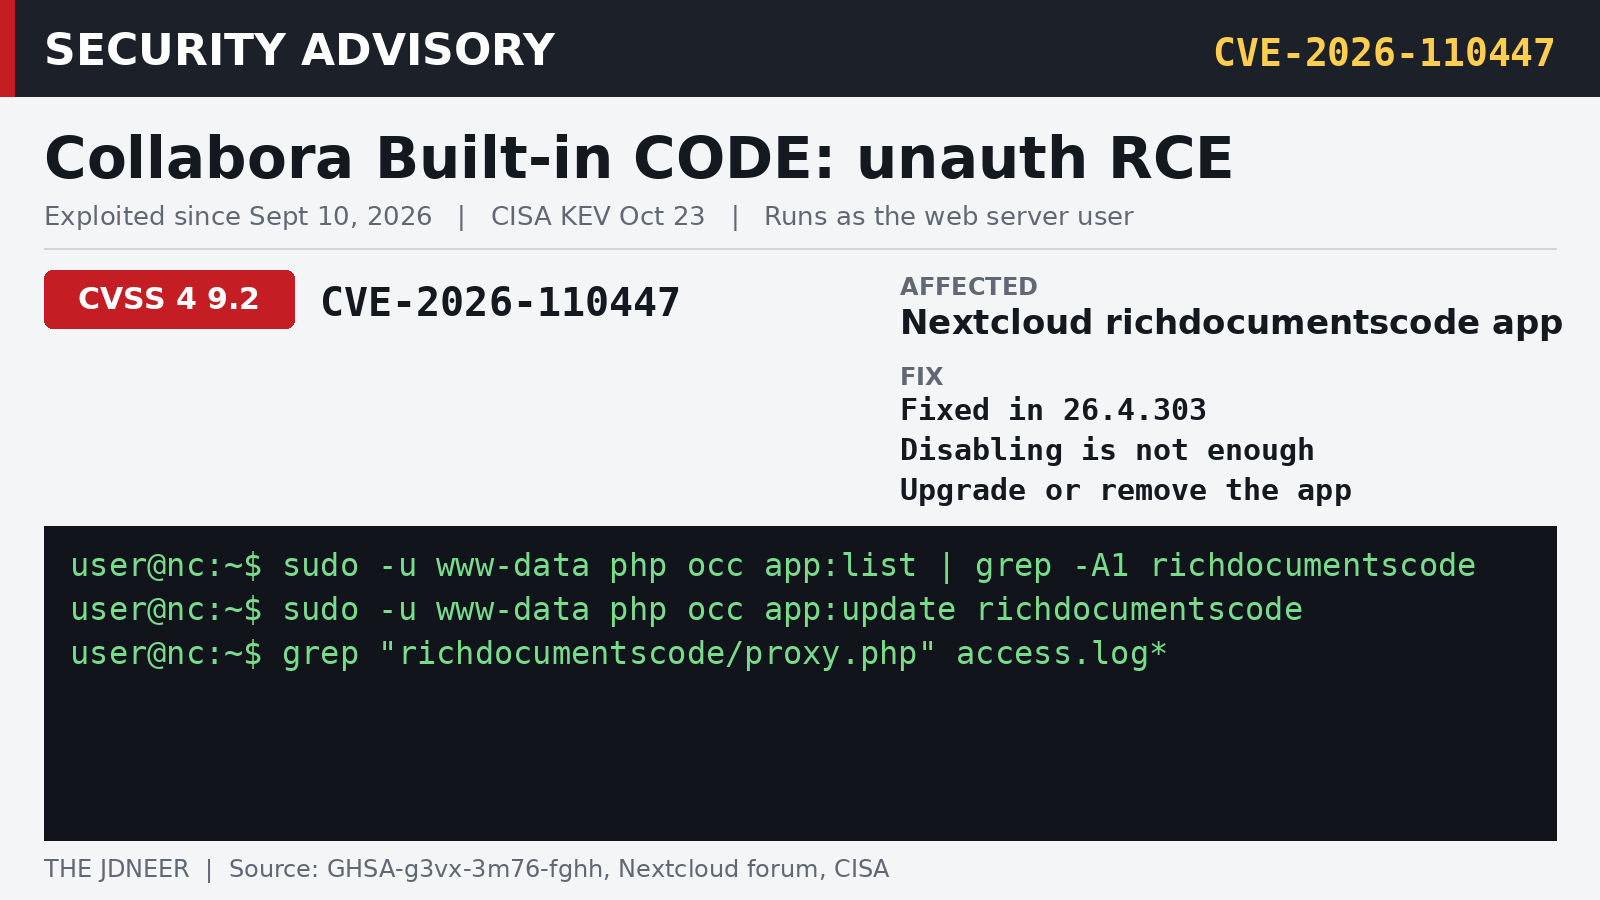
If you run Nextcloud with the Collabora Online Built-in CODE Server app (richdocumentscode), check it today. CVE-2026-110447 is an unauthenticated OS command injection through the app's proxy.php, it is being exploited, and CISA added it to its Known Exploited Vulnerabilities catalog on October 23.
The facts
- Severity: Critical, CVSS v4 9.2. Commands run as the web server user.
- The attack only works while the built-in CODE server is not running: after a container restart, an upgrade, or a crash. Every server goes through that state sooner or later.
- Fixed in richdocumentscode 26.4.303. The CVE record confirms versions before 26.4.303 are affected and that it was exploited in the wild in September and October 2026. The advisory is clear: disabling the app is not enough. Upgrade it or remove it.
- This is a different path from CVE-2025-66208. The fix for that one does not stop this.
- Standalone Collabora Online servers are not the issue here. This is about the built-in app.
What attackers did
According to The Hacker News, the first logged attack was on September 10. Attackers dropped a one-line PHP web shell into the app's folder, and on at least one server used it to search for credential stores and crypto wallets, including KeePass .kdbx files. The Nextcloud community forum posted an "update ASAP" warning.
One trap: Nextcloud 29 and older are end of life, and the app store still serves them an affected version of the app. If you are on 29 or older, upgrade Nextcloud or remove the app.
What I would do
- Search your access logs back to at least September 10 for requests to
richdocumentscode/proxy.php. - Look for unexpected
.phpfiles in the app directory. If you find one, treat the server as compromised: rebuild, and rotate every password and key stored in Nextcloud.
Update it, or remove it if you do not need it:
sudo -u www-data php occ app:update richdocumentscode
sudo -u www-data php occ app:remove richdocumentscode
Check the installed version:
sudo -u www-data php occ app:list | grep -A1 richdocumentscodePaths and the web server user vary by install (Docker, snap, AIO). Adjust the commands to yours.
Sources: CVE-2026-110447 record; Collabora advisory GHSA-g3vx-3m76-fghh; richdocumentscode 26.4.303 release; Nextcloud community forum; CISA KEV alert, Oct 23, 2026; The Hacker News.
More like this
- HTTP2Shell (CVE-2026-111497): What the Brotli Decoder Bug Really Hits, and How to Patch
- Package Cooldowns Compared: GitHub Package Firewall vs. What npm, pnpm, Yarn, Bun, pip, uv and Poetry Already Do
- Your Mesh VPN Agent Is Root on Every Box. Tailworm Is the Reminder.
- eMudhra Broke Almost Nothing, and Still Dented the Chain of Trust