Blog
Security, networks and the occasional questionable decision, mostly with the Philippines in view.
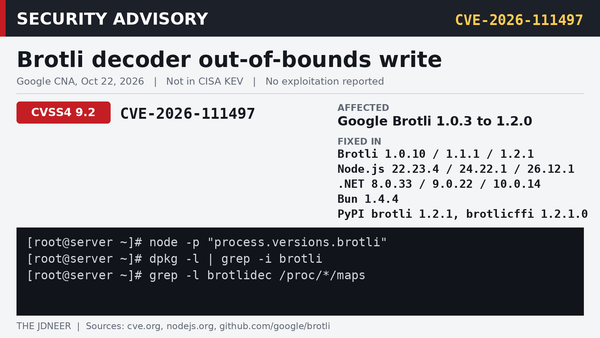
HTTP2Shell (CVE-2026-111497): What the Brotli Decoder Bug Really Hits, and How to Patch
CVE-2026-111497 is an out-of-bounds write in Google's Brotli decoder, 1.0.3 through 1.2.0. Fixed in 1.0.10, 1.1.1 and 1.2.1, plus Node.js, Bun, Python, Envoy and .NET updates. You are exposed if you decode untrusted Brotli data. Not in CISA KEV.
Package Cooldowns Compared: GitHub Package Firewall vs. What npm, pnpm, Yarn, Bun, pip, uv and Poetry Already Do
GitHub now offers an install-time firewall for npm, free in preview and metered later. Most package managers already ship a free cooldown. Here is what each tool does, the copy-paste config, and where cooldowns stop helping.
Your Mesh VPN Agent Is Root on Every Box. Tailworm Is the Reminder.
A researcher showed one hacked Tailscale node reaching root on other servers through Tailscale SSH forwarding. No patch yet. Here is why mesh VPN agents deserve the same suspicion as any privileged daemon.
eMudhra Broke Almost Nothing, and Still Dented the Chain of Trust
Eight eMudhra intermediate CA keys turned out to be numbers under 256. Browsers blocked them within hours, almost no site broke, and eMudhra is leaving the TLS business. The service impact was tiny. The lesson for the chain of trust is not.
The Threat Was Already Badged In: Insider Lessons From Two Lab Poisoning Cases
A Wyoming grad student is accused of poisoning an officemate, and the internet already called it espionage. The charge says assault. What the court record actually shows, and the access, procurement, and reporting controls that would have caught it sooner.
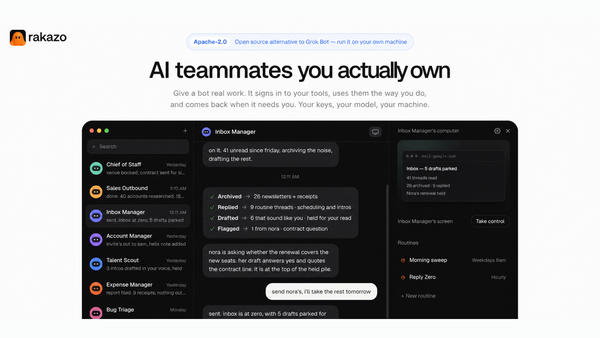
Rakazo v0.3.3: What's New in the Self-Hosted Grok Bot Alternative
Rakazo, the open source, self-hostable AI agent platform, shipped v0.3.3 on October 22. A small release: delete chats on mobile, Telegram replies with images and files, and a handful of fixes.
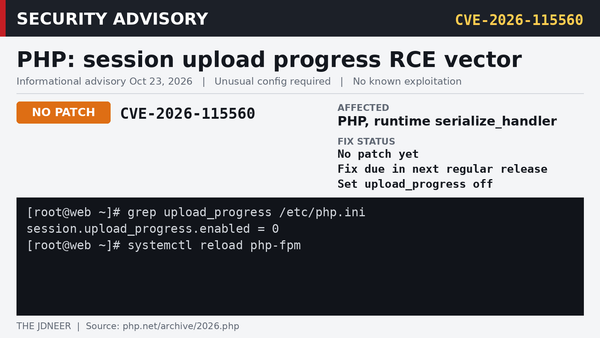
PHP CVE-2026-115560: Disable Session Upload Progress Until the Next Release
PHP.net recommends setting session.upload_progress.enabled=0 to block an unlikely RCE vector, CVE-2026-115560. No patch yet; the fix comes in the next regular release. Only apps that switch serialize_handler to php at runtime are exposed.
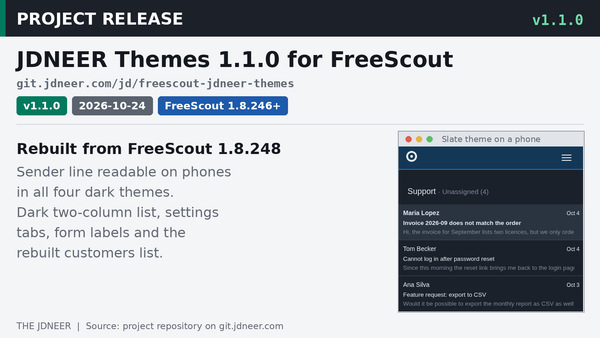
JDNEER Themes 1.1.0: FreeScout Dark Themes Fixed for Phones and Rebuilt for 1.8.248
JDNEER Themes 1.1.0 is rebuilt from FreeScout 1.8.248. It fixes the sender line on phones in all four dark themes, darkens the two-column list, settings tabs and customers list, and now needs FreeScout 1.8.246.
Quad9 Leaves France: When a DNS Resolver Becomes a Censorship Tool
A Paris court ordered Quad9 to block IPTV piracy domains for beIN. Rather than lie to its users or apply French law to the whole world, Quad9 will stop serving France on November 24. Why resolvers are the wrong place to fight piracy.
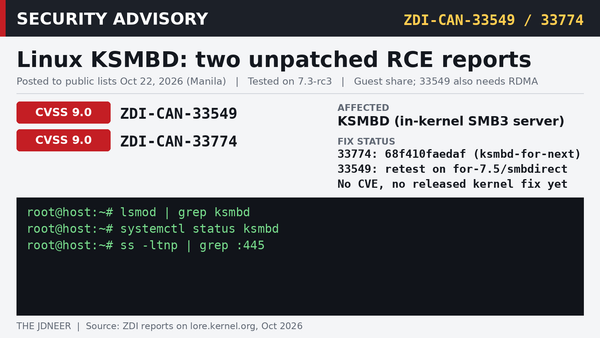
Unpatched KSMBD Bugs Hit Public Kernel Lists: What It Means for You
Trend Micro ZDI copied unpatched Linux kernel bug reports, including two CVSS 9.0 KSMBD flaws, to public mailing lists. Greg Kroah-Hartman objected. The exposure is narrow: only hosts running the in-kernel SMB server. Here is how to check.