Blog
Security, networks and the occasional questionable decision, mostly with the Philippines in view.
DITO CME elects four new directors at annual stockholders' meeting
DITO CME Holdings elected Oozi Cats, Xinxin Wang, Enrique Pampolina and Cenon Audencial Jr. to its board, as Eric Recto and Salvador Medialdea ended their terms.
TESDA's two-day cyber workshop is a start. Let's not call it a cyber skills push
A two-day workshop for TESDA's own ICT staff is a reasonable start, not a national cyber skills effort. Here is what would build real capability.
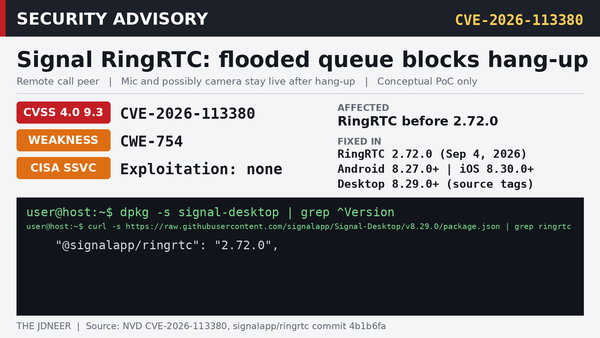
Signal Bug CVE-2026-113380 Could Keep Your Mic Live After You Hang Up
A RingRTC flaw rated CVSS 9.3 let a malicious Signal caller flood the call state machine so your hang-up never landed, keeping the mic and possibly the camera live. It was fixed in RingRTC 2.72.0 on September 4. Here is how to check your app.
The downfall of bgp.exchange: how a volunteer peering exchange lost its domain, mail and management plane in a day
In September 2026 a volunteer peering exchange lost its domain, mail and management plane in about a day. A timeline from public records.
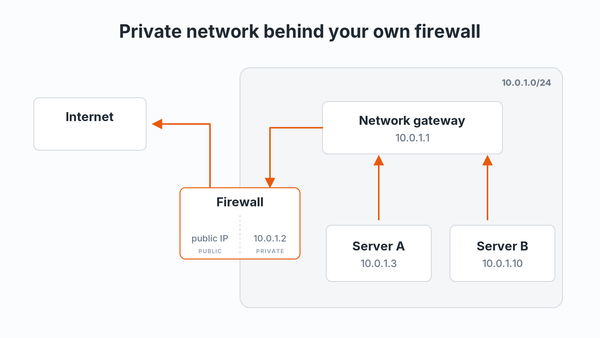
Building a Private Network on Hetzner Cloud Behind Your Own Firewall
Keep servers off the public internet: a Hetzner Cloud private network with one route, your own firewall as the gateway, and working configs for Ubuntu and Rocky Linux 8.
A Third of Philippine Businesses Now Use AI, but Only 17% Have a Plan to Scale It
An AWS-commissioned study says 32% of Philippine businesses now use AI, up from 21% a year ago. But only 17% have a roadmap to scale it, and just 19% feel ready for agentic AI. Skills remain the biggest gap. Here are the numbers that matter.
Denmark's CPR Breach Is a Warning About Government Data Hoarding, and PhilSys Should Take Note
Outsiders pulled names, addresses and ID numbers of about 8.8 million people from Denmark's CPR register through one small company's lookup account, caught only by an invoice. Here is why central registers worry me, and what PhilSys can learn.
Chainguard Broke the PHP Embargo by Six Hours. That Was the Wrong Call
Chainguard shipped fixed PHP images more than six hours before the coordinated October 21 release, citing exploits in the wild. Here is how embargoes work, what Chainguard says, and why I still think releasing early was the wrong call for open source.
Your Car's App May Be the Bigger Privacy Leak: Study Maps Where 21 Cars and 30 Apps Send Data
Northeastern researchers tracked network traffic from 21 cars and 30 automaker apps. Most cars reached third parties, but the apps did more damage: seven sent VINs and other personal data to ad and analytics firms, and Honda changed its app in response.
Scammers Are Posing as BSP Officials, Complete With Fake IDs. Here Is How to Spot Them
The Bangko Sentral ng Pilipinas warns that fraudsters are posing as its officials with fake IDs and forged signatures, asking victims to send money to release or recover funds. BSP staff never ask for payments. Here is how the scam works and what to do.